Physical Address
304 North Cardinal St.
Dorchester Center, MA 02124
Physical Address
304 North Cardinal St.
Dorchester Center, MA 02124
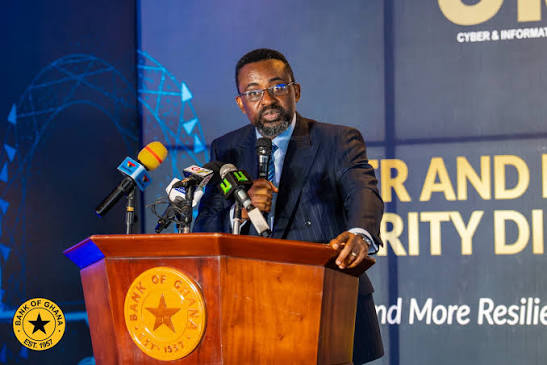
The Bank of Ghana (BoG) is set to conduct targeted reviews of banks’ compliance with its revised Cyber and Information Security Directive as concerns grow over digital fraud, cyber threats and risks associated with online financial services.
Governor of the Bank of Ghana, Dr Johnson Pandit Asiama, announced the planned reviews at the 43rd Annual General Meeting of the Ghana Association of Banks in Accra.
The reviews will assess how banks are implementing the revised directive, which is intended to strengthen cybersecurity standards and improve the resilience of financial institutions as technology continues to transform the banking sector.
Dr Asiama said cybersecurity, data protection, cloud computing, reliance on third-party service providers and operational resilience were receiving increasing attention from the central bank’s supervisory teams.
“Digitalisation is transforming financial services. It has improved efficiency, convenience and financial inclusion, but it has also created new channels through which risks can emerge,” he said.
The planned reviews form part of the central bank’s broader efforts to ensure that financial institutions can identify, manage and respond to emerging digital risks.
As banks expand mobile banking, digital payments and other technology-driven services, their exposure to cyberattacks, data breaches, service disruptions and fraud can also increase.
The revised Cyber and Information Security Directive, introduced in 2026, establishes updated expectations for regulated financial institutions. It places emphasis on governance, accountability, risk management and stronger cybersecurity capabilities.
Dr Asiama said the Bank of Ghana had continued working with the Ghana Association of Banks and other industry stakeholders to support implementation of the directive.
The upcoming reviews will provide the regulator with an opportunity to assess banks’ compliance and identify areas where further improvements may be required.
The BoG Governor urged bank boards and senior management to treat cybersecurity and operational resilience as core business risks rather than issues that should be left solely to information technology departments.
He said the changing financial environment required institutions to strengthen their risk-management frameworks and prepare for emerging threats.
This approach places responsibility on senior leadership to ensure that cybersecurity is incorporated into business strategy, governance, investment decisions and operational planning.
For banks, a cyber incident can have consequences beyond technology systems. It may affect customer confidence, interrupt transactions, expose sensitive information and create financial or reputational losses.
The central bank’s position reflects the need for institutions to prepare for incidents and maintain essential services even when their systems face disruption.
The BoG has identified several areas requiring greater supervisory attention as financial institutions become more digitally connected.
These include:
Third-party risk is particularly important because banks increasingly depend on external providers for software, digital platforms, infrastructure and other services. Weaknesses in a provider’s systems can create risks for the financial institution that relies on it.
The revised directive also introduces a more risk-sensitive approach to implementation, recognising that financial institutions differ in size, complexity, technological maturity and exposure to cyber threats.
The Bank of Ghana launched the revised Cyber and Information Security Directive in March 2026 as an update to its earlier cybersecurity framework.
The directive is designed to move the financial industry beyond basic compliance towards stronger, more active cyber resilience.
It also addresses emerging areas such as artificial intelligence and machine learning governance, alongside cloud security and board-level oversight of cyber risks.
The framework requires regulated financial institutions to strengthen their capabilities, manage risks across their organisations and conduct due diligence on third-party service providers.
The central bank has also emphasised the importance of protecting sensitive financial data and ensuring that technology adoption is consistent with Ghana’s legal and regulatory requirements.
The directive applies to regulated financial institutions, with implementation requirements assessed according to institutional risk profiles and the applicable regulatory framework.
Digital financial services have expanded access to banking and made transactions more convenient for customers and businesses.
Mobile applications, electronic payments and other digital channels allow customers to conduct transactions without always visiting physical branches.
However, these developments have also created new opportunities for fraudsters and cybercriminals to exploit weaknesses in systems or deceive customers.
A successful cyberattack or prolonged service disruption can affect customers, merchants and other institutions connected to the banking system.
The Bank of Ghana’s planned reviews signal that cybersecurity will remain a key part of financial-sector supervision as institutions continue investing in digital services.
For customers, stronger institutional safeguards can help reduce risks, although individuals must also remain alert to phishing messages, suspicious links, fraudulent calls and requests for confidential banking information.
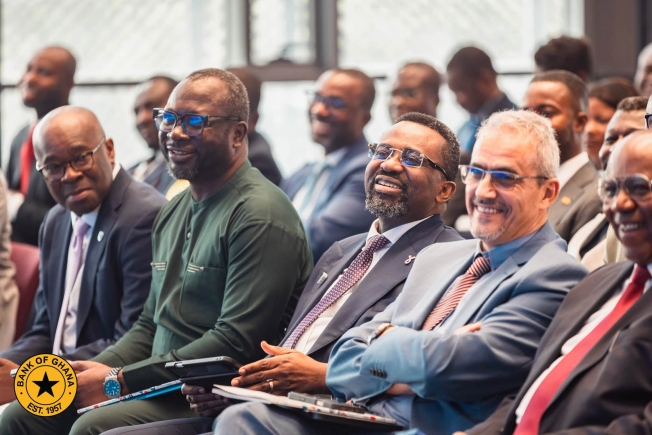
The announcement was made during the 43rd Annual General Meeting of the Ghana Association of Banks, which also marked the launch of the sixth edition of the GH Bankers’ Voice magazine.
The meeting provided a platform for discussions on the relationship between banks and the regulator, as well as the challenges and opportunities facing Ghana’s financial industry.
The cybersecurity agenda reflects the growing importance of cooperation between the central bank, commercial banks and other financial-sector stakeholders in addressing risks that can affect the wider financial system.
The planned thematic reviews are expected to give the Bank of Ghana a clearer picture of how financial institutions are implementing the revised cybersecurity requirements.
The exercise may also help identify weaknesses and areas where banks need to improve their governance, security controls and response plans.
The announcement does not, by itself, indicate that any particular bank has breached the directive or that penalties have been imposed.
Rather, it signals an increased supervisory focus on compliance and preparedness as digital financial services become more widespread.
As Ghana’s banking sector continues to modernise, the effectiveness of cybersecurity controls will be important in maintaining public confidence, protecting financial information and supporting a stable digital financial system.
African360 WhatsApp Channel for more News update: https://whatsapp.com/channel/0029Vb7Oc6nGk1FpdCN0xn44